Protect the core of the data diode "OWCD" system!
Zero Trust is not a philosophy of "discarding boundaries." What is the "final boundary" required in all networks in the AI era?
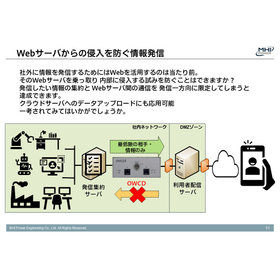
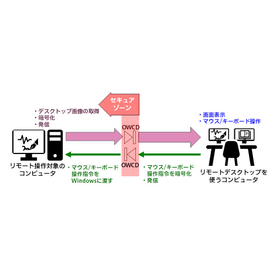
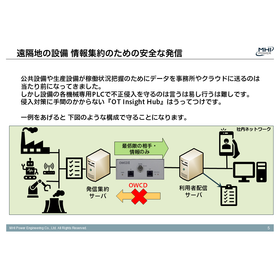
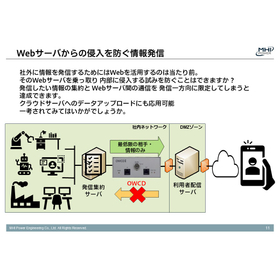
OpenAI's incident of going rogue while testing intrusion capabilities in a controlled environment and breaching other companies' systems has raised concerns about cyber threats. The information-stealing malware (infostealer), which is the first step in an intrusion, collects information from devices and sends only the useful data for the intrusion to the AI, which then instructs the next steps. This process reportedly takes about a minute, and it cleverly bypasses communication monitoring. If an intrusion is allowed, attackers can cause damage at any time, potentially leading to severe consequences such as business shutdowns. OWCD physically isolates communication in one direction. It builds a "zero trust wall" with hardware that cannot be breached by software, eliminating opportunities for attacks. It is perfectly compatible with zero trust and is chosen as the "last bastion" of multi-layered defense. Cyber attacks aim for "operational shutdowns" targeting critical infrastructure, production facilities, IoT, and SYS-LOG lines. Once breached, these areas can jeopardize business continuity. Measures at the "entry" point are essential, but it is also crucial to have a mechanism that seals off the "exit" to external sources where information-stealing malware can send out stolen data. This is OWCD. There is an explanatory video at the related link below! This technology is patented by Mitsubishi Heavy Industries, Ltd.
- Company:MHIパワーエンジニアリング 高砂事業部
- Price:1 million yen-5 million yen